Services

Services

Azure / Entra, Red Team, and pentest. Wireless and social engineering as Red Team add-ons. Every engagement is custom-scoped.

01 / Cloud

Azure and Entra ID Assessments

Identity is the new perimeter. We assess Azure and Entra ID tenants the way an attacker approaches them: token theft and replay, consent and application abuse, conditional access gaps, privileged role paths, and hybrid trust between on-prem Active Directory and the cloud.

  • Entra ID
  • Token abuse
  • Conditional Access
  • Consent phishing
  • Hybrid AD trust

Read the page

02 / Red Team

Red Team

One stated objective. Full path. We measure whether you detect and contain it. Phishing and wireless are add-ons, not separate products.

  • Initial Access
  • Persistence
  • Defense Evasion
  • Lateral Movement
  • Objective-Based Intrusion

Read the page

03 / Pentest

Penetration Testing

We perform comprehensive penetration tests targeting web applications, internal and external networks, cloud infrastructures, and mobile platforms. Our goal is to identify vulnerabilities before attackers do.

  • Web applications
  • Internal networks
  • External networks
  • Cloud
  • Mobile

Read the page

04 / Simulation

Adversary Simulation

SOC detection and response under a multi-stage intrusion. Usually run as part of a Red Team engagement.

  • SOC detection
  • Incident response
  • Multi-stage intrusion
05 / Emulation

Adversary Emulation

Custom scenarios matched to your threat profile. Same family as Red Team.

  • APT emulation
  • Threat profiling
  • Custom TTPs
06 / Wireless

Wi-Fi Security Assessments

Available as a red-team add-on. WEP through WPA-Enterprise, rogue APs, and man-in-the-middle against wireless infrastructure.

  • Password cracking
  • Rogue access points
  • Man-in-the-middle
07 / Human

Social Engineering

Available as a red-team add-on. Phishing campaigns, impersonation, and the human path into the environment.

  • Phishing campaigns
  • Impersonation
  • Awareness training

Tooling

ANIMO

Azure Network Intel & Mission Ops

A tool we built and use on Azure and Entra assessments. One operator interface for tokens, tenant enumeration, and post-exploitation. It is not the engagement. We are.

  • Capture, exchange, mint and analyse OAuth tokens, including access, refresh, PRT and SAS
  • WhoAmI discovery with derived capability verdicts and fine-grained ARM action enumeration
  • Reach Outlook, Calendar, Teams, OneDrive, SharePoint, Storage and Key Vault through Graph and ARM
  • Remote execution over Azure VM runCommand, uploaded webshells and SSTI payloads
  • Entra device registration for certificate-based persistence, TAP issuance and auth-method backdoors
  • Password, SPN and refresh-token sprays, with engagement report generation

C++17 / Qt 6. Source on GitHub

ANIMO dashboard

Command and Control

Pickle

Cross-platform C2, Windows / macOS / Linux

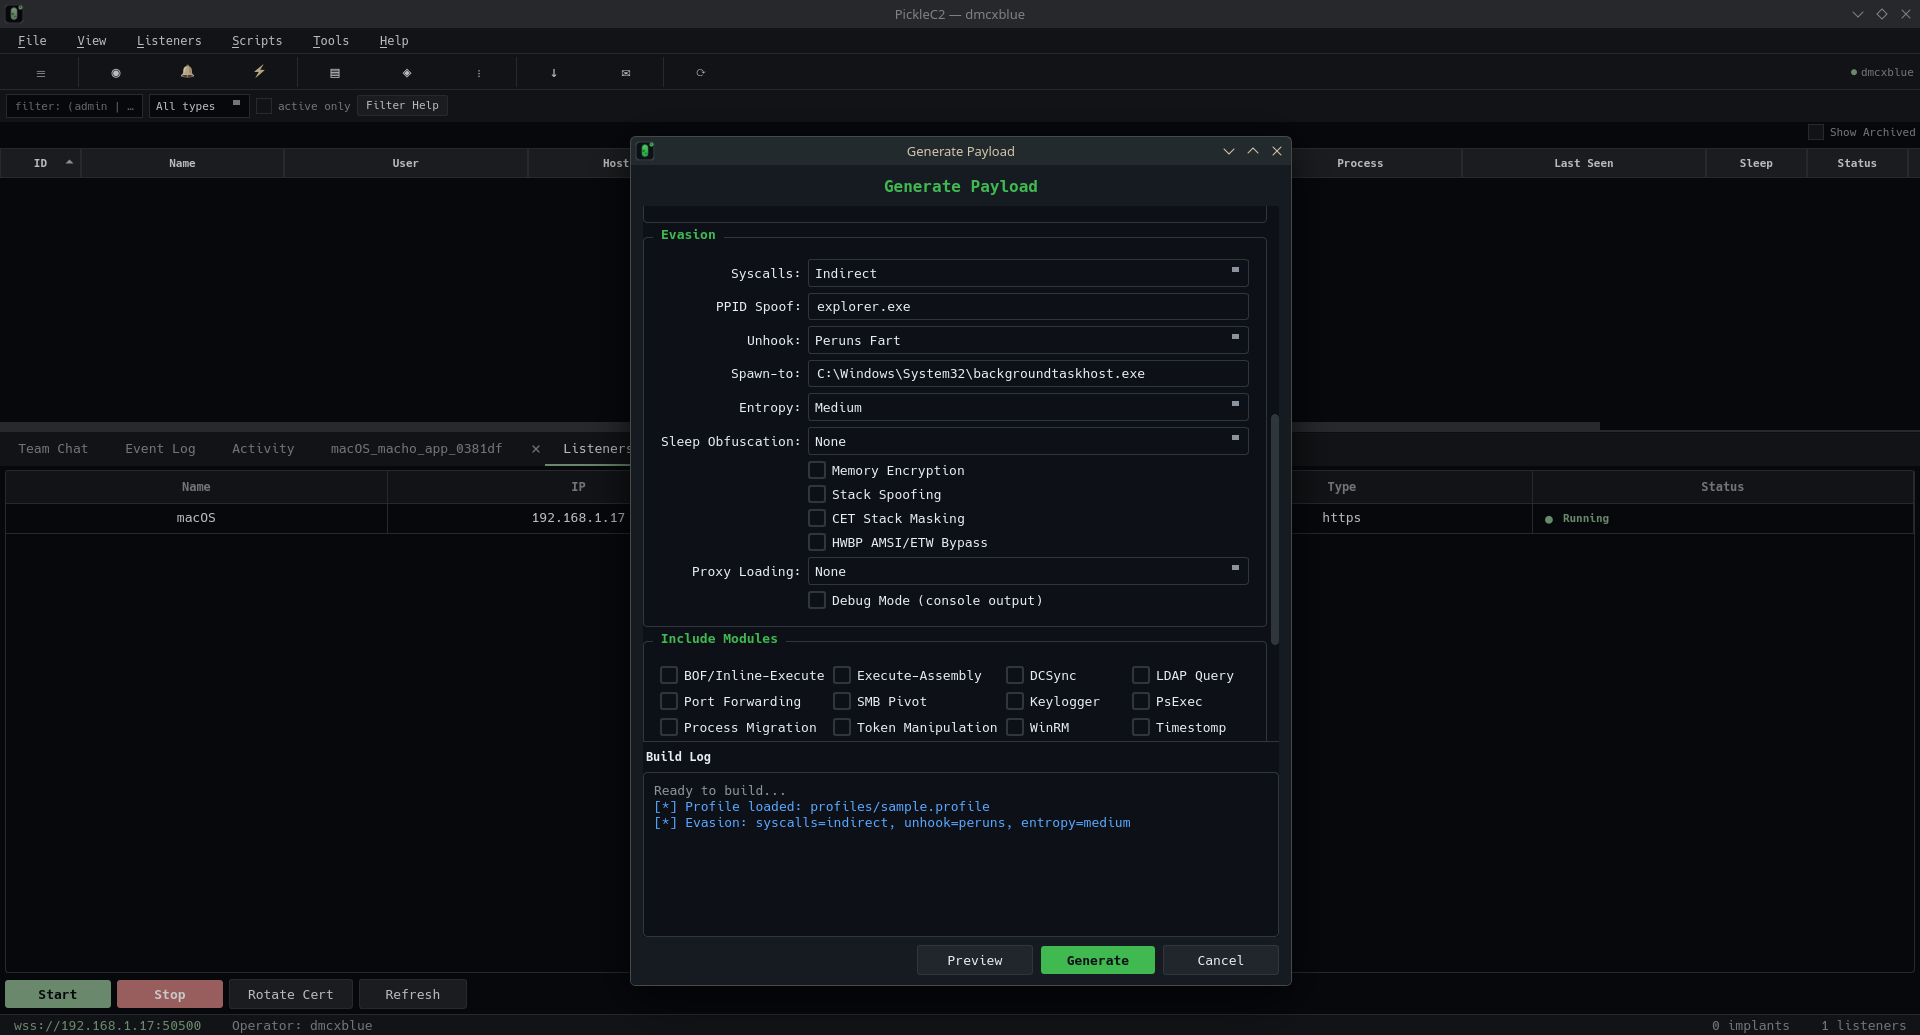
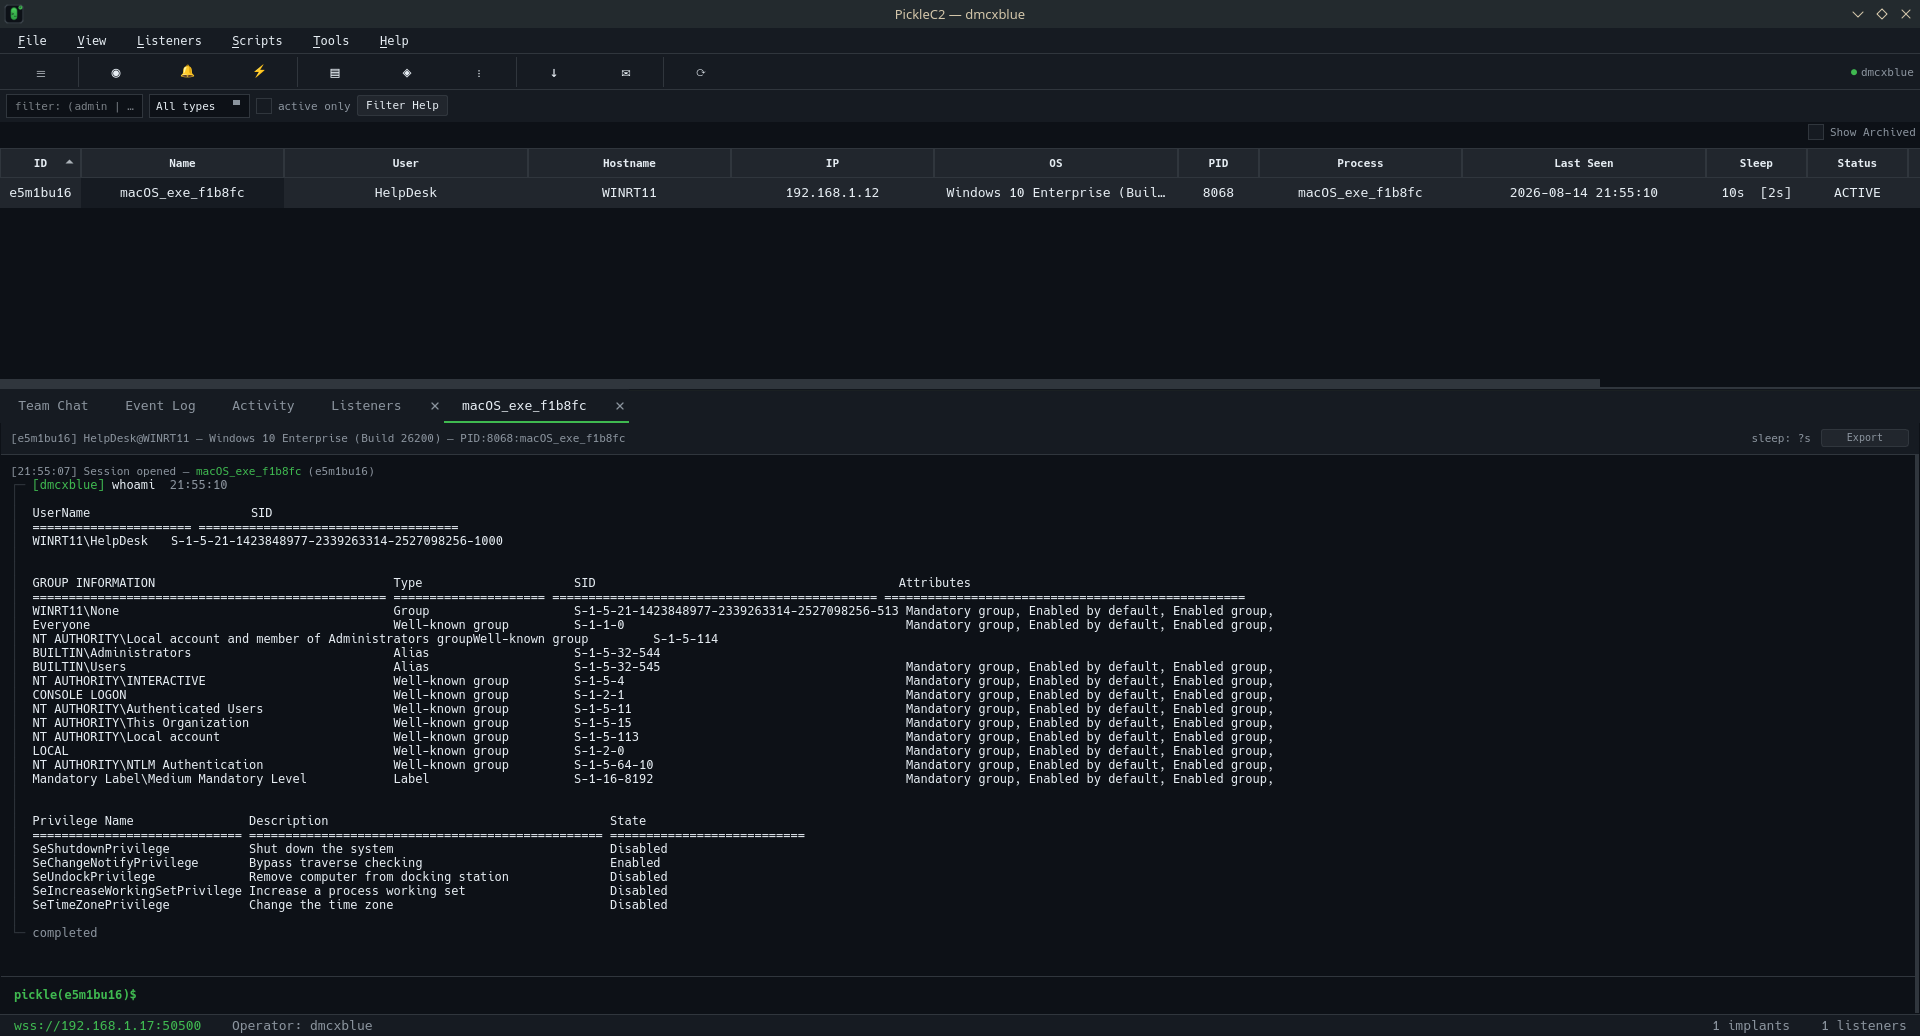
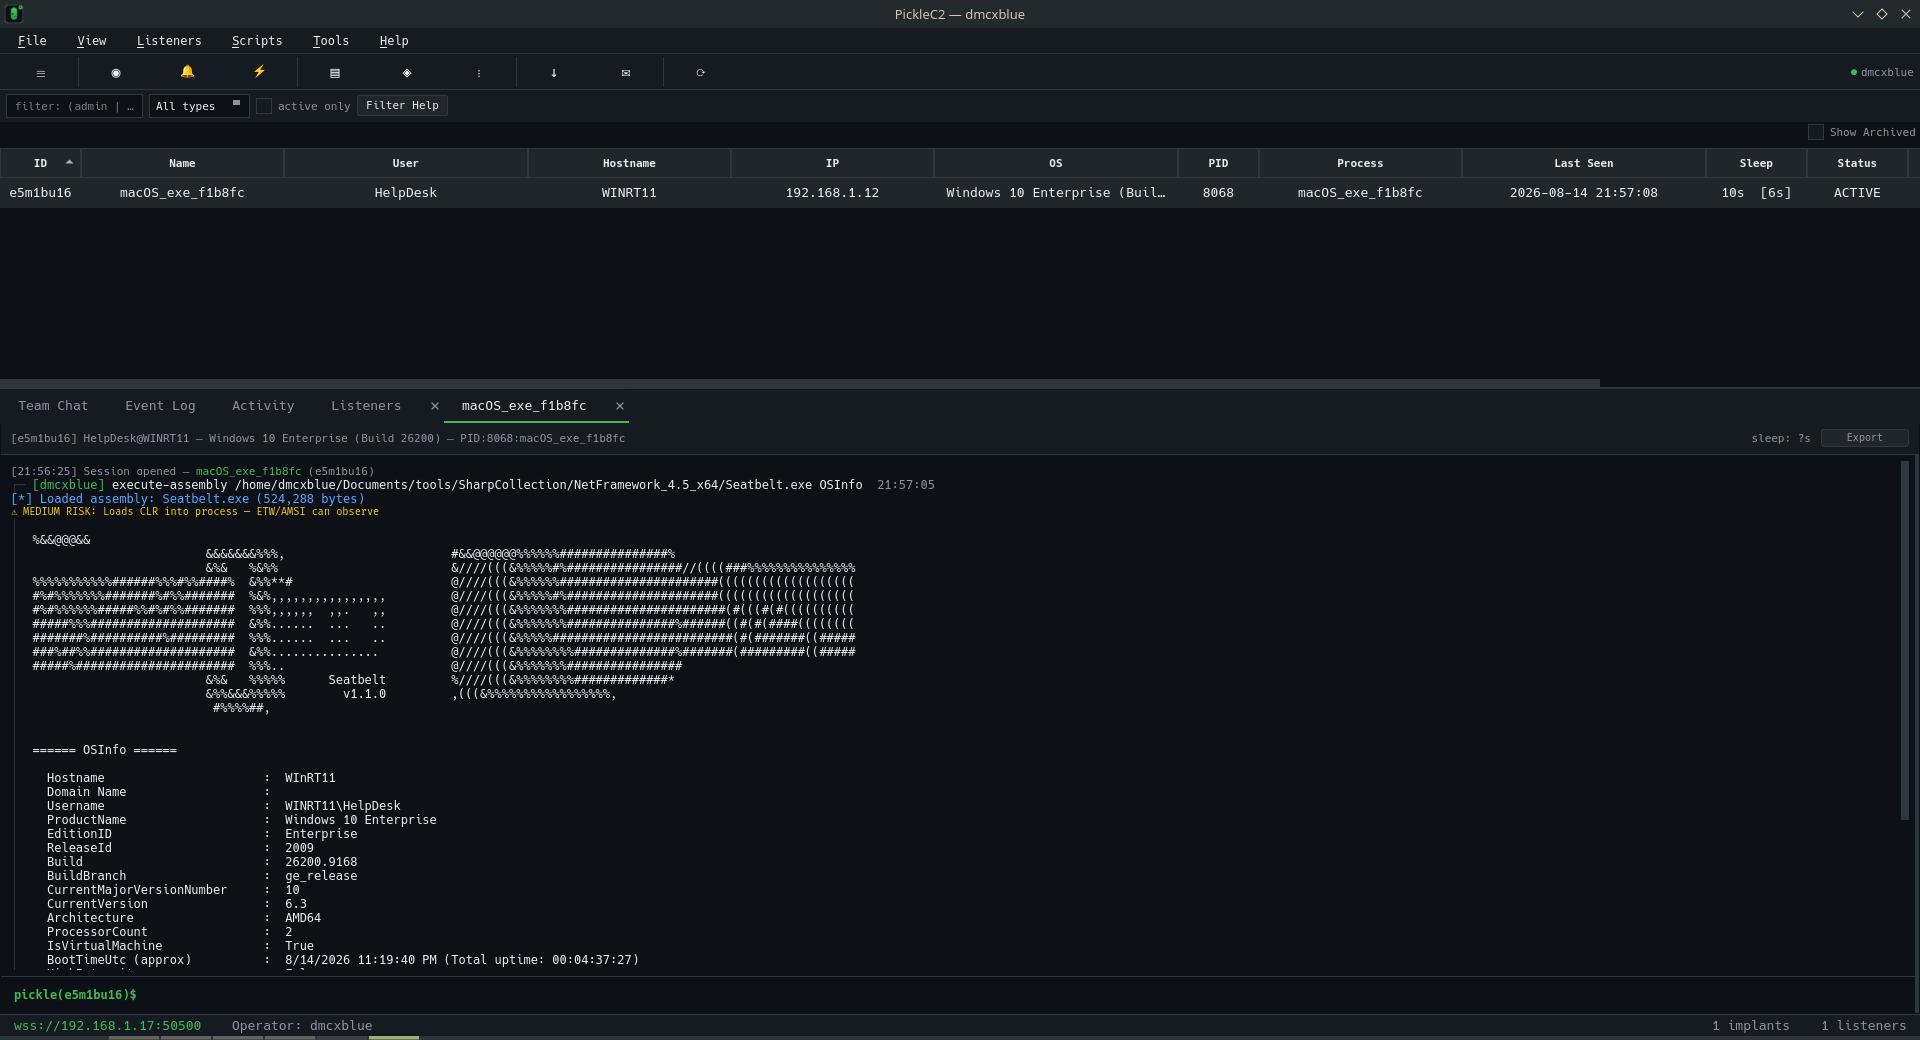
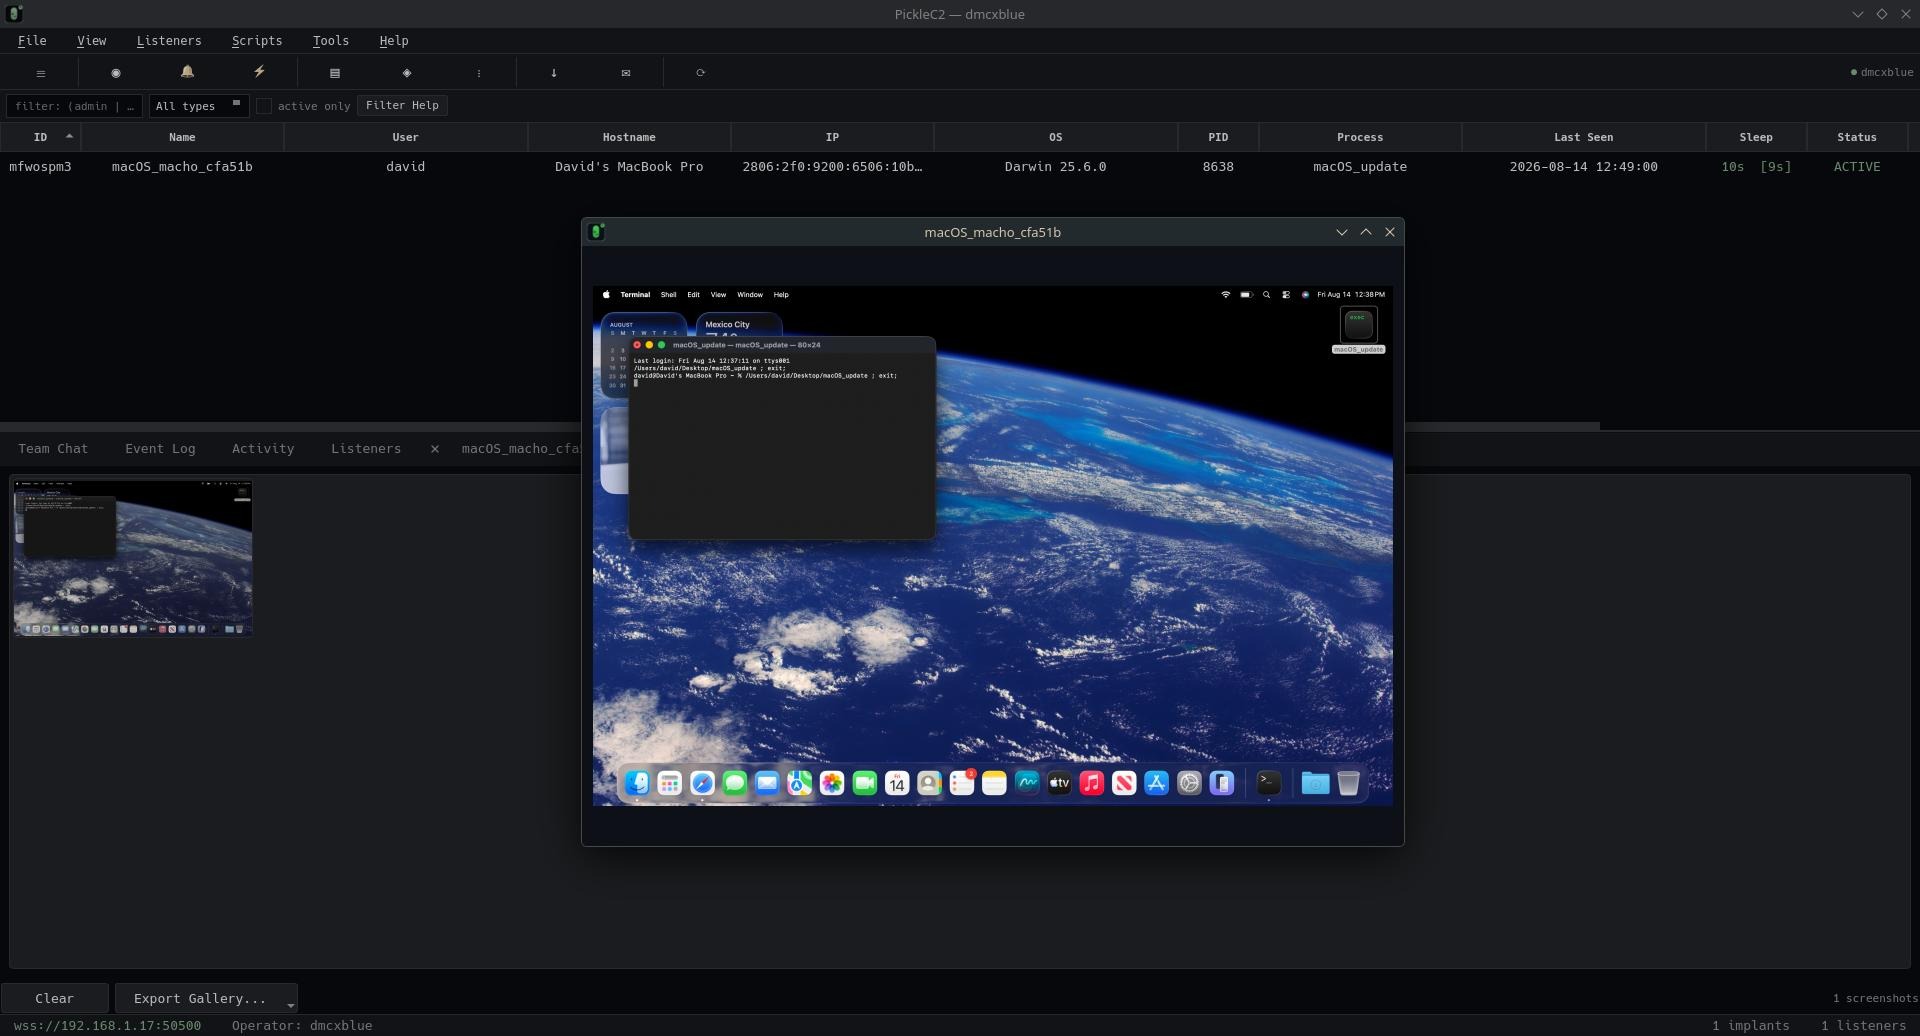
Our own command and control framework, built in-house and used on engagements. Full-scope operations from initial access through to objective, run on infrastructure we stand up ourselves. We build the infrastructure, we operate the implants, and we document every step so your team can rebuild the timeline afterwards.

implant generation
implant generation
whoami BOF
whoami BOF
execute assembly OPSEC awareness
macOS implants
macOS implants

MITRE ATT&CK Enterprise

Aligned to the framework

Engagements map to ATT&CK tactics so findings land in the same language your blue team already uses.

10 of 14 tactics shown. Every technique links to MITRE ATT&CK.

Contact

Written scope. Then the work.

Tell us what you want tested. A 20-minute call, then a written Statement of Work covering targets, rules of engagement, and out of scope.